Jensen Huang resigns as Nvidia CEO after admitting an affair
Nvidia's chief executive stepped down this month after acknowledging an affair with a woman U.S. intelligence reportedly suspected of Chinese ties, prompting renewed attention to executive security and counterintelligence risks across corporate America.
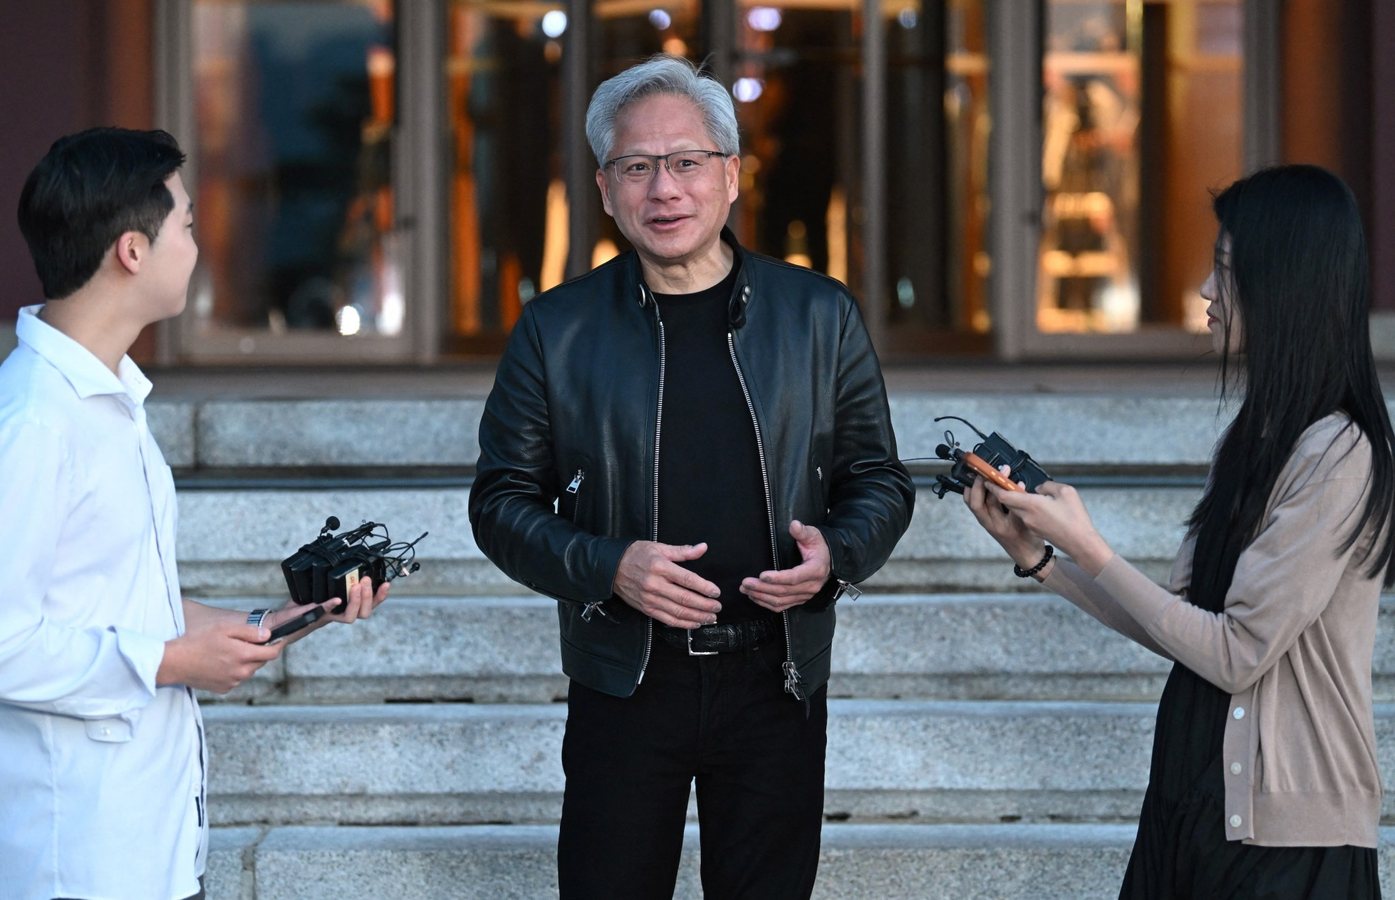
Jensen Huang resigned as chief executive of Nvidia this month after admitting an affair, a departure that has drawn attention to the personal and security risks facing senior executives in the technology industry. The affair partner was reportedly under suspicion by U.S. intelligence of having ties to Chinese intelligence. Nvidia's board has said it found no evidence that national security or company secrets were compromised. China has denied the allegations.
The episode arrives as artificial intelligence companies increasingly find themselves targeted by rivals and foreign governments. Last month, OpenAI's countermeasures team found a listening device hidden in a conference room in San Francisco. The FBI later arrested an OpenAI employee accused of planting it. Taken together, the two cases have pushed security specialists to argue that boardrooms and executive suites need the same kind of protection that has long been standard in government and defense work.
Security has become a visible line item for large companies. Nvidia spent nearly $4 million on Huang's protection in fiscal 2026, up from $3.5 million in 2024. The spending reflects a broader trend. According to Equilar proxy data, about 38 percent of S&P 500 companies gave some executives security perks in 2025, up from 28 percent in 2023. The concern is not hypothetical: UnitedHealthcare chief executive Brian Thompson was killed in Manhattan in December 2024, an attack that intensified debate over how exposed top executives are in public life.
Specialists say physical bodyguards address only part of the problem. The biggest vulnerability, according to those who advise companies, is predictability. Executives who follow the same routes, schedules and routines make themselves easy to track, and their residences are often easier targets than corporate offices. Travel is another pressure point. Advisers recommend counterintelligence briefings before trips abroad, along with loaner devices that carry no sensitive data.
Technology is also changing the threat. Deepfake voice clones can be built from only seconds of publicly available audio, and in tests, people identified live video deepfakes correctly only about half the time. That makes impersonation of executives, whether to authorize payments or extract information, a growing concern for security teams.
To reduce the risk of insider threats, experts recommend layered hiring screening that includes background, financial and social media checks, and sometimes polygraph examinations. They also urge periodic post-hire reviews, particularly when an employee's personal circumstances change in ways that could signal vulnerability to coercion. Yet business schools rarely teach security, with Northwestern's Kellogg School cited as an exception. Experts argue that companies need coordination among physical security, cybersecurity, legal and communications teams, so that a single incident is not handled in isolation.
Source: fortune.com
15